Network level DDoS protection
Block harmful online traffic before it reaches your business
Overview
Protection built into your connection
A Distributed Denial of Service (DDoS) attack floods your internet connection with malicious traffic, making websites, applications and online services unavailable.
Most DDoS protection sits behind your connection, reacting once malicious traffic has already arrived. Vorboss works differently.
Because we own and operate the network, we identify and filter malicious traffic before it reaches your connection.

Always stay online

Gain full threat visibility

Block attacks instantly







Protection options
Full protection
Flood protection
Ideal for customer-facing services, VPNs and critical applications
Ideal for standard business connectivity
Unlimited mitigations
Unlimited mitigations
Up to 5 days of scrubbing each month
N/A
Edge filtering
Edge filtering
Traffic scrubbing
N/A
Includes scrubbing centre protection
Blocks common volumetric attacks
Features

Network-level filtering
Malicious traffic is blocked upstream before it reaches your connection.

Automatic detection
Attacks are identified and mitigated without waiting for you to report them.

24/7 proactive monitoring
Our Network Operations Centre (NOC) watches over the network around the clock, immediately investigating anything that needs attention.

Unlimited mitigations
Protection remains active no matter how often your business is targeted.

Traffic scrubbing
Complex attacks are cleaned while legitimate traffic continues flowing.

Real-time visibility
Understand attack activity and mitigation through traffic analytics and reporting.
Why Vorboss?
Why businesses choose Vorboss?
Most DDoS protection reacts once harmful traffic has already reached your connection. Ours doesn't. Because we own our network, we have total visibility, meaning we can stop the attack before it reaches your business.
We're a London business operating exclusively on our own London network. This gives us full visibility into local traffic and a unique context on regional threat patterns.
We step in to mitigate immediately. Because we own and operate our network end-to-end, we have full visibility into every area and can get to the root of the problem much faster.

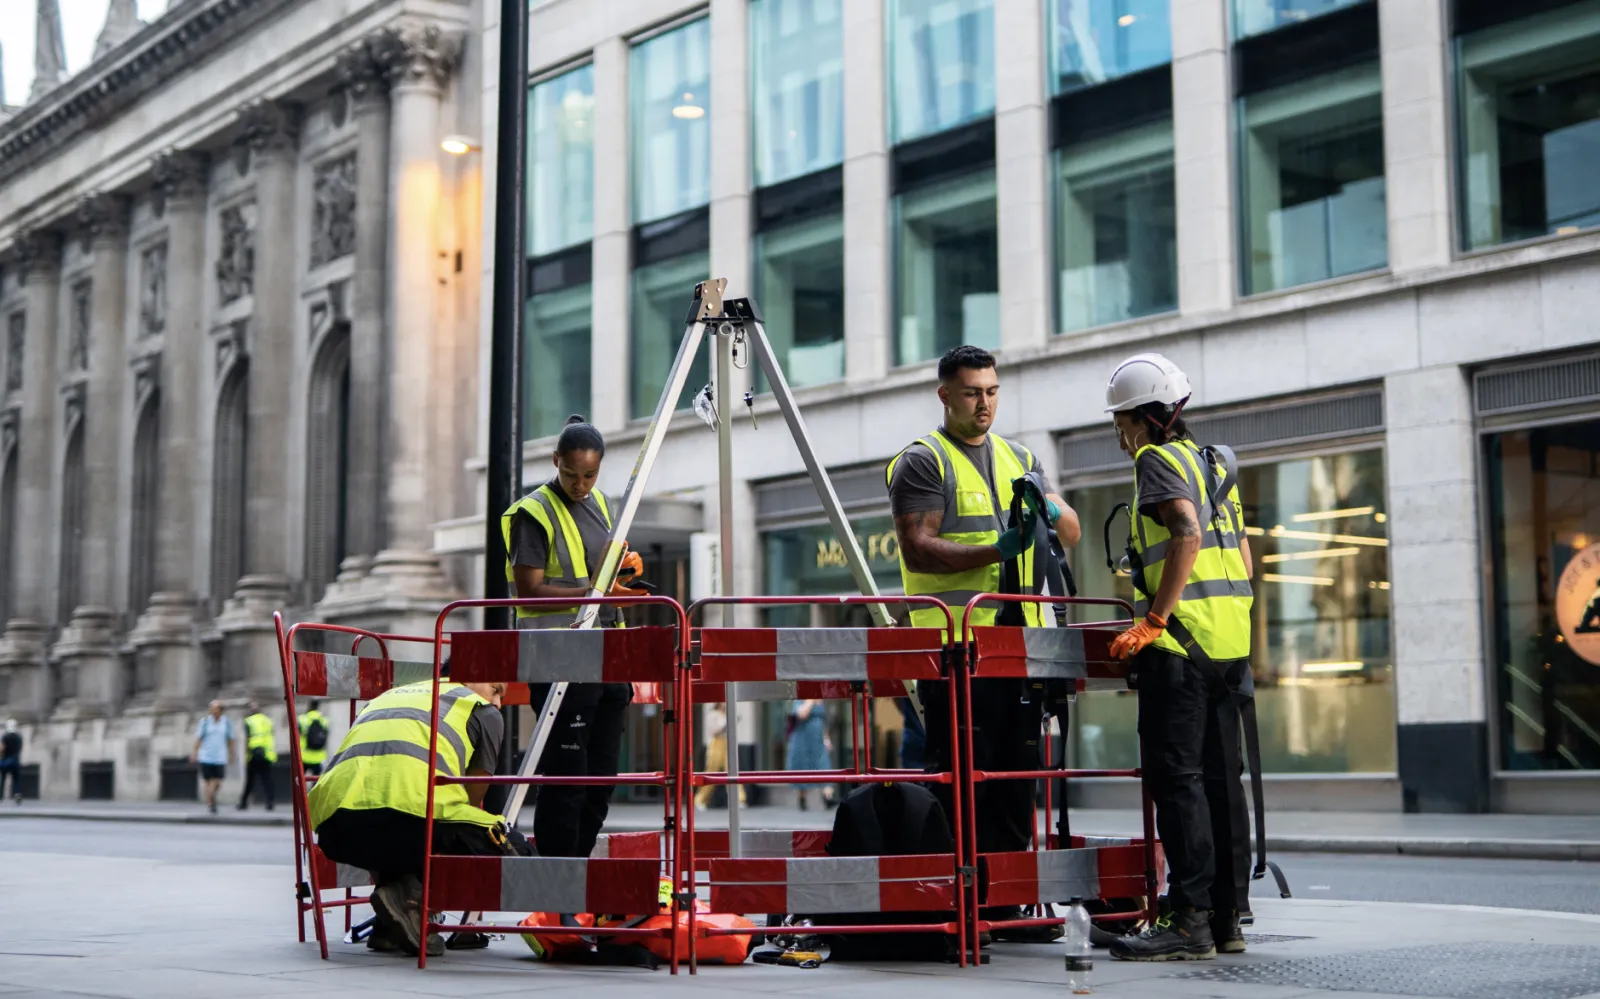
We operate exclusively on our own London network
This gives us full visibility into local traffic and a unique context on regional threat patterns.
1,000km
of fibre
100Gbps
Capable
1,400+
BUILDINGS CONNECTED
Our own systems have been independently tested to verify they meet recognised cybersecurity standards.
We follow internationally recognised information security practices to keep your data and information protected.
Also certified to ISO 9001, ISO 14001 and ISO 22301.

In-house cybersecurity
Your service is delivered by our own cybersecurity experts, with no outsourced support or third-party handovers.

One number to call
From monitoring and updates to reporting and support, one expert team manages everything from start to finish.
"The speed of delivery and level of service blew us away; getting online in just 3 weeks was a huge relief."
Hasan Khalifah, Finance Partner

“There was real relief knowing Vorboss would take care of everything in-house and liaise directly with the necessary stakeholders.”
Andy Simpson-Pirie, Chief Technology Officer
"We have been working with Optimity, now Vorboss, for nearly three years.
Over this time, they have truly understood our business and have offered insight into improving our internal processes as well as introducing major technical change and deep technical support."
Koto

“Vorboss’ impressive internet service and customer experience gave us the confidence to bring them into further projects."
Tim Head, Global Service Delivery Head

"The Vorboss team are friendly and professional to work with. They handle complex IT work confidently while keeping day-to-day support running smoothly."
Stan Tang, Chief Operating Officer
"The flexibility to upgrade quickly and having our own dedicated lines were big selling points for us."
Zafar Shah, IT UX Manager

"Vorboss has become a trusted IT management partner helping us work towards cyber compliance in a heavily regulated sector."
Cyted Health
"Even if another provider could beat Vorboss on price, which hasn’t happened yet, we’d happily stick with them purely for the service and reliability."
Delal Miah, Head of IT
"Vorboss has always taken our IT seriously, helping us use technology to our advantage."
Vertical Aerospace
"Vorboss took the time to understand our business, not just sell us a service."
Jon Dobson, Partner and Lead Colourist
"Vorboss took over our IT infrastructure during a period of significant change and quickly adapted to our evolving needs with professionalism and flexibility."
J T Walton, Head of Shared Services

"It’s been truly refreshing dealing with Vorboss, who have been efficient throughout the onboarding process."
Fred Webster-Trussell, Managing Director

"Our experience with Vorboss has been nothing short of exceptional!"
Alan Farbrother, Head of IT


Let's get you connected
Fill in the form to chat with us
FAQ
Have a question?
We've got you covered.
DDoS (Distributed Denial-of-Service) protection safeguards your business's online services by detecting and mitigating malicious traffic aimed at overwhelming your network. Implementing DDoS protection is crucial to maintain service availability, prevent revenue loss, and uphold your company's reputation.
Our DDoS protection service continuously monitors network traffic in real-time, identifying unusual spikes or patterns indicative of an attack. Upon detection, malicious traffic is redirected through scrubbing devices that filter out harmful data while allowing legitimate traffic to proceed, ensuring minimal disruption to your operations.
Yes, our DDoS protection service is compatible with all Direct Internet (IPX) and Protected Internet (IPP) services, providing seamless integration with your current network infrastructure.
Our comprehensive DDoS protection defends against various attack types, including volumetric, protocol, and application-layer attacks, ensuring robust security across all network layers.
Flow sampling involves analysing metadata from a statistical sample of network traffic, typically around 1 in every 1,000 packets. This method allows for efficient, real-time detection of DDoS attacks without impacting network performance.
Once the attack subsides, our system automatically reroutes traffic back to normal operation without manual intervention, ensuring a seamless transition and continuous service availability.
